http-terminator is PortSwigger’s AI pipeline for discovering HTTP request-smuggling bugs. Which stages run, its dependencies, and its testing limits.
Hash Identifier Tools – Command-Line Password Hash Identification
hashID and Name-That-Hash tested against current password formats. Both miss bcrypt’s $2b$ prefix; only Name-That-Hash recognises Argon2id.
whitelist-bypass – WebRTC Tunnels Through Video-Calling Platforms
whitelist-bypass tunnels traffic through commercial video calls, for networks that allow only approved domains. How its two tunnels work, and the claim to verify.
WRAITH – Browser Hooking and Blind XSS Page Mirroring
WRAITH combines BeEF-style browser hooks with blind-XSS capture and a credentialed Page Mirror. Tested locally, with its limits examined.
Praetorian – Offensive Security Tools Built Around Portable Go Workflows
Praetorian’s Go security tools consolidate established offensive workflows, with portable binaries, direct pipelines and a partial shared SDK.
AI IR Overlay – Incident Response Specification for AI Agents
AI IR Overlay specifies containment for agents using valid credentials, with a working kill-switch contract and an admitted gap when no SOC is staffed.
MSSQLand – Lightweight MS-SQL Interaction Tool for Lateral Movement and Post-Exploitation
MSSQLand enables red teams to interact with MS-SQL servers and linked instances in restricted environments without complex T-SQL queries. Assembly-ready tool for lateral movement.
Credential Stuffing in 2025 – How Combolists, Infostealers and Account Takeover Became an Industry
Credential stuffing drove 22% of all breaches in 2025. How combolists, infostealers and ATO tooling are fuelling enterprise account takeover at scale
DumpBrowserSecrets – Browser Credential Harvesting with App-Bound Encryption Bypass
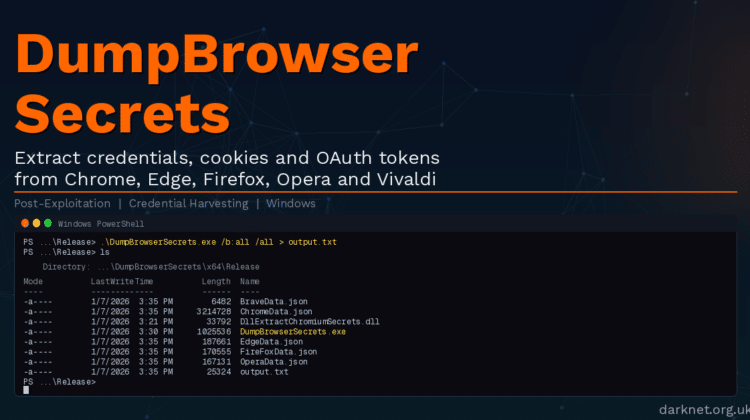
DumpBrowserSecrets extracts saved passwords, cookies, OAuth tokens and autofill data from Chrome, Edge, Firefox, Opera and Vivaldi, bypassing App-Bound Encryption via Early Bird APC injection.
Systemic Ransomware Events in 2025 – How Jaguar Land Rover Showed What a Category 3 Supply Chain Breach Looks Like
Systemic ransomware events in 2025, how Jaguar Land Rover’s shutdown exposed Category 3 supply chain risk, with lessons from Toyota, Nissan and Ferrari.