
This article has been substantially updated after feedback from Envilder maintainer Marçal Albert Castellví. The original June 2025 version incorrectly described the project’s implementation, installation, command syntax and AWS SSM retrieval model. Those errors have been corrected, and the article now covers the significant changes to Envilder since the original publication.
Envilder is a Node.js command-line tool and set of runtime SDKs for mapping application environment variables to secrets held in AWS Systems Manager Parameter Store or Azure Key Vault. It does not introduce another vault or secrets service. The secret values remain with the cloud provider, while a JSON file committed alongside the application records which secret each variable should resolve to.
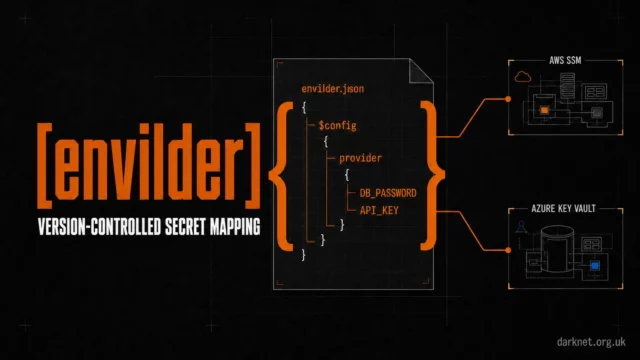
That mapping is the part I missed when I first covered Envilder in June 2025. I described it as fetching parameters recursively from an AWS SSM path and turning them into environment variables. It has never worked that way. Every variable is explicitly declared, so changing which secret an application consumes produces a repository diff that can go through the same review process as an application change.
The project has also moved considerably since that original article. AWS is no longer the only provider, there is now a GitHub Action for CI/CD, and .NET, Python and Node.js SDKs can resolve the same mapping directly at application startup without writing a .env file to disk.
Overview
A normal secret manager answers one part of the configuration problem well: where should the sensitive value live? AWS SSM Parameter Store and Azure Key Vault already provide storage, access controls, auditing and integration with their respective cloud identity systems.
The application still needs to know which value it expects and where to find it. That relationship can end up scattered between deployment scripts, CI configuration, application code and settings changed directly in cloud consoles.
Envilder puts that relationship into an explicit mapping file. A basic AWS configuration looks like this:
|
1 2 3 4 5 |
{ "$schema": "https://envilder.com/schema/map-file.v1.json", "DB_PASSWORD": "/my-app/prod/db-password", "API_KEY": "/my-app/prod/api-key" } |
The names and provider references can be committed safely. The values are still retrieved from the secret store at execution time.
This makes a change from one secret path to another visible in Git. Someone reviewing a pull request can see that DB_PASSWORD now points somewhere different without gaining access to the password itself.
Features
Explicit Secret Mapping
Envilder does not enumerate an SSM hierarchy and infer variable names from whatever happens to be underneath it. Each application variable maps to a specific provider-side value.
On AWS that means individual ssm:GetParameter requests rather than ssm:GetParametersByPath. SecureString parameters are requested with decryption enabled, so the executing identity also needs permission to use the appropriate KMS key where required.
I prefer this design to path discovery for application configuration. It is more verbose, but the repository tells you exactly what the application expects. Adding or removing a secret becomes intentional rather than an accidental consequence of changing the contents of a parameter hierarchy.
AWS SSM And Azure Key Vault
The original release was AWS-only. Envilder added Azure Key Vault support in 2026 and now uses the same mapping model with either provider.
An Azure configuration can declare the provider and vault directly in the mapping:
|
1 2 3 4 5 6 7 8 9 |
{ "$schema": "https://envilder.com/schema/map-file.v1.json", "$config": { "provider": "azure", "vaultUrl": "https://my-vault.vault.azure.net" }, "DB_PASSWORD": "my-app-prod-db-password", "API_KEY": "my-app-prod-api-key" } |
Google Cloud Secret Manager is listed on the project roadmap but is not currently supported.
CLI, CI/CD And Runtime
The same mapping is now consumed in three different places.
The CLI can resolve values into a local .env file. A GitHub Action provides the equivalent mapping for CI/CD. Runtime SDKs for .NET, Python and Node.js can instead resolve the secrets during application startup and keep them in process memory without creating a .env file.
That reuse is probably the most useful improvement since the original release. Local development, a build pipeline and production application startup no longer need three independently maintained descriptions of the application’s secret requirements.
Controlled Push
Envilder can also push values back to the configured cloud provider. That is useful when initially populating an environment or intentionally rotating a value, although I would keep the IAM or RBAC permissions for that operation separate from normal read-only application access.
Installation
Envilder v0.13.0 requires Node.js 22.12 or later. There are no pre-built Go binaries and the old installation command in this article was incorrect.
You can run Envilder directly through npx:
|
1 |
npx envilder --version |
Or install the CLI globally with npm:
|
1 |
npm install -g envilder |
For AWS, configure credentials with permission to read the SSM parameters referenced by the mapping. SecureString values are decrypted automatically when the executing identity has the required KMS permission.
Usage
Create an envilder.json file containing the application’s mappings:
|
1 2 3 4 5 |
{ "$schema": "https://envilder.com/schema/map-file.v1.json", "DB_PASSWORD": "/my-app/prod/db-password", "API_KEY": "/my-app/prod/api-key" } |
Resolve those values from AWS SSM and write the resulting environment file:
|
1 |
npx envilder --map=envilder.json --envfile=.env |
Azure Key Vault can be selected from the command line where the provider is not already defined in the map:
|
1 |
npx envilder --provider=azure --vault-url=https://my-vault.vault.azure.net --map=envilder.json --envfile=.env |
Runtime SDKs
The runtime SDKs remove the intermediate environment file completely.
Python applications can install Envilder from PyPI:
|
1 |
pip install envilder |
Then resolve the application’s mapping during startup:
|
1 2 3 |
from envilder import Envilder Envilder.load("envilder.json") |
The .NET package integrates with the standard configuration system:
|
1 |
dotnet add package Envilder |
It can then add the mapped values directly to application configuration:
|
1 2 3 4 5 |
var config = new ConfigurationBuilder() .AddEnvilder("envilder.json") .Build(); var dbPassword = config["DB_PASSWORD"]; |
Node.js applications have an equivalent SDK:
|
1 |
npm install @envilder/sdk |
Security Relevance
Envilder does not solve secrets management as a whole. AWS IAM or Azure RBAC still decides who can retrieve a value. The underlying provider still owns storage, encryption, auditing and rotation. Envilder will not tell you whether an application has excessive privileges or whether the secret itself should exist.
Its narrower contribution is making the application’s dependency on those secrets explicit.
That becomes useful in environments where configuration otherwise accumulates outside the normal code-review process. If an application’s database credential moves from one secret to another, the mapping changes. If a new third-party API key becomes necessary, another mapping appears. If an application stops needing a secret, the corresponding entry can disappear.
None of those changes reveal the value, but they leave an ordinary Git history showing what the application was configured to consume and when that changed.
This also sits reasonably well with the cloud-native security model. Envilder does not proxy secret requests through another hosted service or require teams to migrate values into a separate vault. Authentication remains AWS or Azure authentication, and access remains visible through the provider’s own audit facilities.
Where It Fits
I would look at Envilder for teams already using AWS SSM Parameter Store or Azure Key Vault but handling secret consumption differently in local development, CI and production.
It is less compelling if you already have a mature secrets platform with application integration, policy enforcement and a well-managed deployment abstraction that provides the same contract. Envilder deliberately does not attempt to compete with HashiCorp Vault or the cloud secret stores themselves.
There is also some operational responsibility in committing the mapping. Secret values are absent, but paths and names can still reveal application structure, service names and the existence of sensitive integrations. That is usually an acceptable trade for an internal repository, but it should not be mistaken for information with zero sensitivity.
Conclusion
Envilder is a better project today than the one I covered in 2025, but the bigger correction is that I misunderstood its original design.
The useful part was never recursively downloading an SSM path. It was making the relationship between an application variable and a specific cloud-managed secret explicit and version controlled.
The additions since then make that model considerably more practical. The same contract can now follow an application from a developer laptop into GitHub Actions and then into .NET, Python or Node.js at runtime, while the actual values remain in AWS or Azure.
That is a relatively small layer in a secrets architecture, which is probably why it is useful. Teams that already trust their cloud provider to hold the secrets do not necessarily need another place to put them. They may just need a better record of which application is supposed to consume what.
You can read the Envilder documentation here: https://envilder.com/
The source code is available on GitHub: https://github.com/macalbert/envilder